IT Documentation: Best Guide to Security & Compliance | GoCo
Poor IT documentation creates security and compliance risks. Learn how better IT records improve visibility, control, and audit readiness. 🔐
Poor IT Documentation Increases Security and Compliance Risks
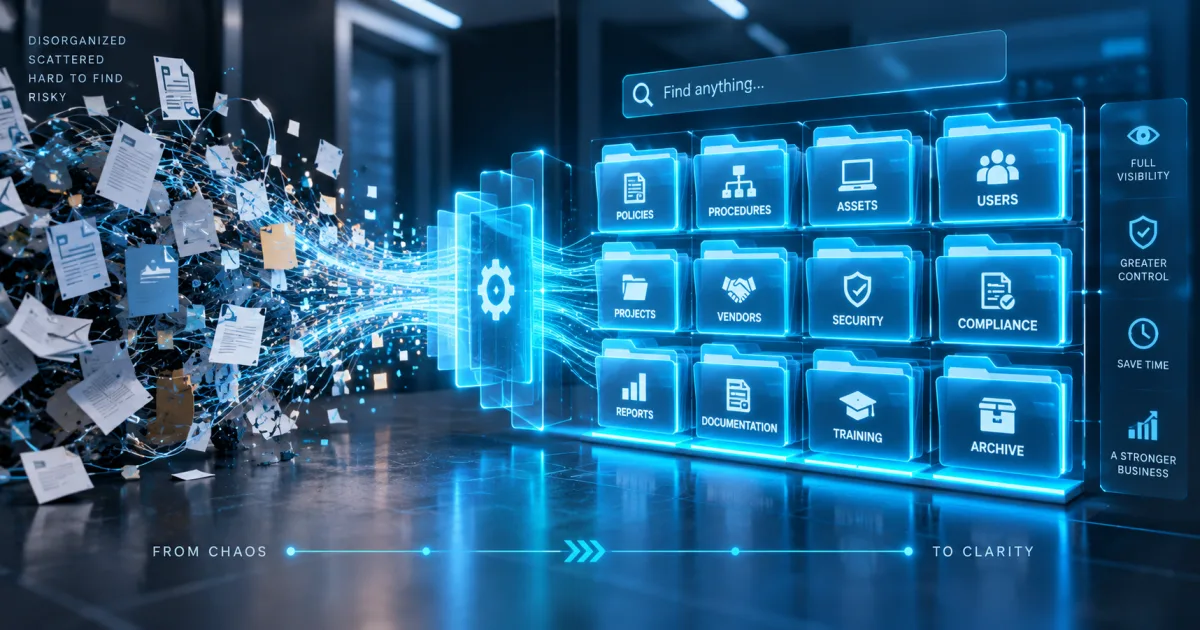
Most companies don’t realize they have an IT documentation problem until something goes wrong. For example, when a key employee leaves, and no one knows how a critical system was configured. When a security audit request arrives, policies can’t be located. If an incident happens, and there’s no clear record of what changed, or when.
In each case, the issue isn’t a lack of technology. It’s a lack of IT documentation.
For growing companies, weak documentation quietly increases exposure to both security and compliance risks. And unlike visible technical failures, documentation gaps accumulate silently until they become operational risks.
What Is IT Documentation? Why is it Often Overlooked?
I.T. Documentation refers to the structured recording of:
- System configurations
- Network architecture
- Access control policies
- Security procedures
- Vendor relationships
- Incident response plans
- Change management logs
It creates visibility into how your I.T. environment operates.
Yet documentation is often deprioritized because it doesn’t feel urgent. Teams focus on deployment, troubleshooting, and scaling systems. Documentation is postponed for “later.”
The Security Risk of Informal Knowledge
In many small to medium-sized businesses, critical I.T. knowledge lives in:
- A senior engineer’s memory
- An email thread
- A shared spreadsheet
- A vendor portal
This informal approach creates dependence on individuals rather than systems. When documentation is incomplete:
- Security configurations cannot be verified
- Access permissions are not reviewed consistently
- Incident response becomes slower
- Configuration drift goes unnoticed
Security depends on consistency, and consistency depends on documentation.
Poor IT Documentation Weakens Security
1. Untracked Access and Permissions
Without documented access policies:
- Privileged accounts accumulate
- Temporary access becomes permanent
- Offboarding processes miss systems
Over time, this leads to unnecessary exposure. Proper IT documentation ensures that access controls are visible, reviewable, and enforceable.
2. Configuration Drift
Cloud environments and hybrid infrastructures change frequently. Without documentation:
- Security settings differ across environments
- Patch levels are inconsistent
- Firewall rules are unclear
- Endpoint security policies vary
Configuration drift increases risk because no one can confidently verify whether systems meet security standards.
3. Delayed Incident Response
In a security incident, time matters. If system diagrams, escalation procedures, or vendor contacts are undocumented:
- Response is slower
- Investigation is incomplete
- Recovery is prolonged
Good IT documentation reduces uncertainty during high-pressure moments.
Compliance Risks Caused by Documentation Gaps
Security and compliance are directly connected. Frameworks such as SOC 2, HIPAA, and other regulatory standards require:
- Documented policies
- Evidence of control implementation
- Audit trails
- Change management records
Even if security controls are technically in place, without documentation, they cannot be validated. Auditors do not assess assumptions. They assess evidence.
Poor IT documentation turns compliance from a manageable process into a reactive scramble.
The Hidden Cost of Poor Documentation
The cost of weak documentation rarely appears immediately. It shows up over time through:
- Repeated mistakes
- Redundant work
- Failed audits
- Lost deals due to security concerns
- Overreliance on specific individuals
As technology environments grow more complex, undocumented systems become harder to manage. Scaling without documentation multiplies operational risk.
Documentation as a Security Control
IT documentation is not administrative overhead; it is a security control, supporting:
- Accountability
- Visibility
- Risk management
- Consistency
- Business continuity
When documentation is integrated into project workflows and change management processes, it reduces the likelihood of both security incidents and compliance failures.
Why Growing Companies Struggle With I.T. Documentation
SMBs often face:
- Limited internal I.T. resources
- Rapid growth
- Frequent system changes
- Competing priorities
In these environments, documentation feels secondary to execution. But growth without documentation creates fragile infrastructure. As team size increases, institutional knowledge fragments. The risk grows with it.
How to Strengthen IT Documentation
Improving documentation does not require heavy bureaucracy. It requires structure. Start with:
- Centralizing documentation in a secure, accessible repository
- Defining ownership for documentation updates
- Documenting onboarding and offboarding procedures
- Maintaining network and system diagrams
- Logging configuration changes
- Reviewing documentation quarterly
Documentation should be integrated into every I.T. project—not treated as an afterthought.
The Role of Project Management
Project Management plays a critical role in documentation discipline. Without structured project workflows:
- Documentation tasks are skipped
- Updates are inconsistent
- Security reviews lack context
With structured execution:
- Documentation is part of deliverables
- Changes are recorded systematically
- Security and compliance are embedded in workflows
Documentation becomes part of the process, not a separate burden.
The GoCo Perspective
At GoCo, we view IT Documentation as foundational to secure and scalable infrastructure. By combining:
-
Project Management
-
I.T. consulting
-
Security-first design
We help organizations move from informal knowledge to documented control. Technology evolves, teams change, and vendors rotate. Documentation preserves clarity across those transitions.
Poor IT documentation rarely causes immediate disruption. It increases risk gradually, through invisibility.
Security and compliance require visibility, and we all know that visibility requires documentation.
If your organization is growing, the best strategic time to strengthen documentation is before complexity makes it difficult to do so.
Technology enables operations, and documentation protects them.
With us, You’re in Good Company.
Technology decisions shouldn't be based on trends; they should support better business outcomes.
Explore our latest LinkedIn articles, where we share practical insights on Managed IT Services, cybersecurity, governance, operational excellence, and strategies that help businesses reduce risk and scale with confidence.
Because better decisions start with better understanding.
Good Company IT
GoCo
You are in Good Company