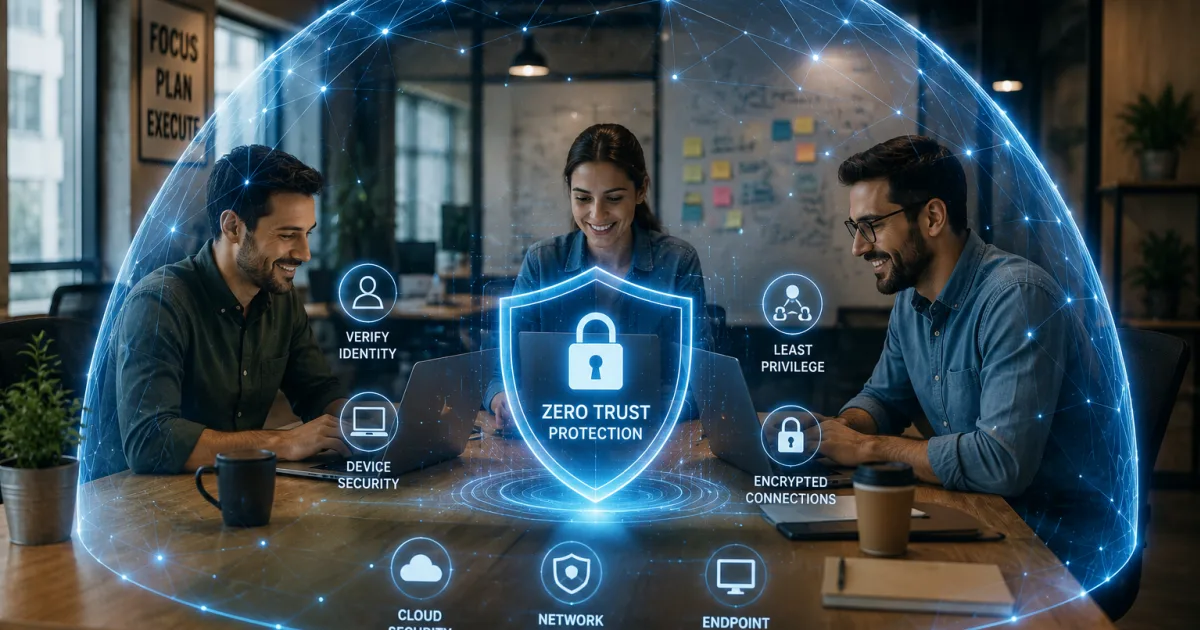
Zero-Trust Security: How to Protect SMBs | GoCo
Zero-Trust Security helps SMBs reduce cyber risk and strengthen IT security. Protect your business before it's too late. Learn more 🔒💻
Has this ever happened to you? It’s a regular working day, everything seems fine. Your team logs into their cloud tools, emails are flowing, and operations look smooth—until one compromised credential opens a backdoor into your system. No alarms. No warnings. Just silence… until the ransomware hits. This is exactly why Zero-Trust Security has become critical for SMBs operating in today’s increasingly connected and complex IT environments. Unfortunately, this is something that happens on a regular basis.
What Is Zero-Trust Security?
Zero-Trust isn’t just another cybersecurity buzzword. It’s a complete architectural shift in how organizations think about access, data, and verification.
The traditional security model, the one built on firewalls, passwords, and the idea that “inside the network = safe” no longer holds up. Modern IT ecosystems are hybrid, cloud-based, and interconnected. Employees work remotely, third-party apps plug into critical systems, and sensitive data moves between dozens of endpoints.
Zero-Trust flips the script.
Instead of assuming users or devices are trustworthy by default, Zero-Trust operates on one principle: Never trust. Always verify.
Every access request, whether it’s an employee connecting from the office, a remote contractor, or a cloud integration, must be continuously verified before permission is granted.
The Core of Zero-Trust: Verification and Micro-Segmentation
To understand Zero-Trust, it helps to look at the technical foundation:
- Identity and Access Management (IAM)
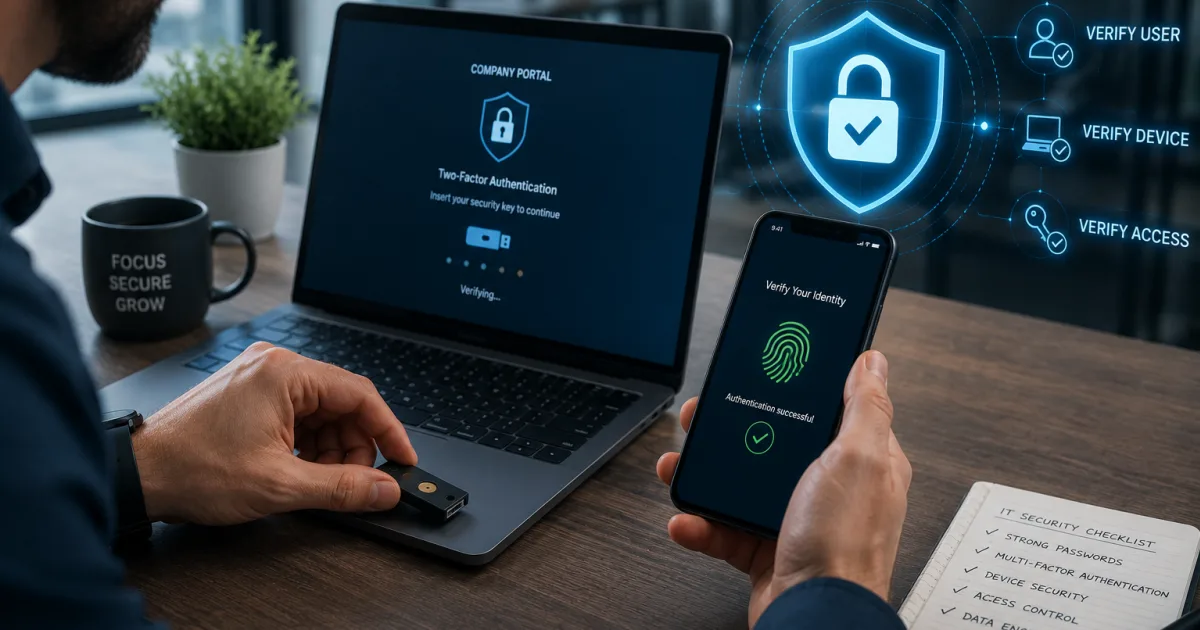
Zero-Trust starts with who is trying to access what. Strong IAM solutions integrate multi-factor authentication (MFA), least privilege policies, and behavioral analytics to detect anomalies in login patterns.
- Network Segmentation
Instead of one large, open network, Zero-Trust uses micro-segmentation—breaking systems into isolated zones. Even if an attacker breaches one segment, lateral movement across the network is contained.
This is where the Server Message Block (SMB) protocol becomes relevant.
The Hidden Risk in Server Message Block (SMB) Protocol
Server Message Block (SMB) is one of the most widely used network protocols in business environments. It allows applications and systems to read and write files, share printers, and communicate over a network.
However, its popularity also makes it a prime attack vector.
Legacy SMB versions, especially SMBv1, have known vulnerabilities that have been exploited in some of the world’s most infamous cyberattacks, including WannaCry and NotPetya.
Why SMB Matters in Zero-Trust
In a Zero-Trust model, every communication path—especially something as central as SMB—must be authenticated, encrypted, and monitored.
- Unsecured SMB connections can allow lateral movement within your network, letting attackers pivot from one compromised machine to another.
- Unpatched SMB servers often expose sensitive data or credentials.
- Improper SMB configurations can bypass access controls, directly conflicting with Zero-Trust principles.
Implementing Zero-Trust without addressing SMB traffic is like locking your front door while leaving the windows open.
Common SMB Vulnerabilities Threatening SMBs
Even if your business has strong firewalls and antivirus tools, SMB misconfigurations can quietly undermine your entire security posture. Here’s how:
-
Open SMB Ports (TCP 445): Many small businesses leave port 445 open to the internet, creating an easy entry point for attackers to exploit SMB weaknesses.
-
Outdated SMB Versions: Using SMBv1—deprecated since 2017—is still surprisingly common in older systems and embedded devices. Attackers specifically scan for these legacy endpoints.
-
Unencrypted SMB Traffic: Without SMB encryption (introduced in SMB 3.0), attackers can intercept or modify data in transit.
-
Weak or Shared Credentials: If SMB shares rely on outdated user credentials or shared accounts, Zero-Trust cannot function properly.
-
Unmonitored File Shares: Data exposure often comes from internal file sharing where permissions are overly broad.
How Zero-Trust Fixes SMB Security Gaps
The beauty of Zero-Trust is that it doesn’t just add another tool; it changes how every tool, including SMB, behaves inside your IT environment.
Here’s what that looks like in practice:
- Enforce Identity Verification Everywhere
Integrate your SMB authentication with centralized identity providers (e.g., Azure AD, Okta). Require MFA for all user access, even for internal shares.
- Encrypt SMB Communication
Enable SMB encryption on all critical servers and disable legacy SMBv1 protocols. Encryption ensures that even intercepted traffic is unreadable.
- Apply Network Segmentation
Separate file servers, application servers, and workstations using VLANs or firewalls. This prevents compromised devices from spreading infections laterally.
- Implement Continuous Monitoring
Use Endpoint Detection & Response (EDR) and Security Information & Event Management (SIEM) tools to track SMB activity patterns. Suspicious logins, brute force attempts, or large data transfers should trigger alerts.
- Automate Patch Management
Zero-Trust thrives on automation. Regularly update SMB services, operating systems, and firmware to eliminate known vulnerabilities.
The Cost of Ignoring Zero-Trust
Some SMBs hesitate to invest in Zero-Trust because it sounds “enterprise-grade.” But here’s the reality:
- 60% of SMBs that suffer a major cyberattack close within six months.
- The average cost of downtime now exceeds $9,000 per minute for mid-sized businesses.
- Compliance frameworks like HIPAA, SOC 2, and ISO 27001 are increasingly emphasizing Zero-Trust principles for data protection.
The real expense isn’t in implementing Zero-Trust—it’s in recovering from not having it.
And the ROI? It’s not just about avoiding breaches. It’s about scaling securely**,** maintaining client trust**,** and protecting your operational bandwidth so your team can focus on innovation, not damage control.
Beyond Firewalls: Building a Zero-Trust Culture
Technology alone won’t secure your business. Zero-Trust is as much a cultural shift as it is a technical framework.
- Educate employees about phishing, password hygiene, and secure access practices.
- Limit privileges to only what’s needed. Even trusted employees shouldn’t have unrestricted access.
- Review vendor access regularly. Third-party integrations are one of the fastest-growing threat surfaces.
Think of Zero-Trust as a mindset: everyone must earn their access—every time.
Implementing Zero-Trust with a Managed IT Partner
For many SMBs, building an internal Zero-Trust framework can feel overwhelming. It requires specialized skills across identity management, endpoint protection, compliance, and network architecture.
That’s where partnering with a Managed Service Provider (MSP) like GoCo changes the equation.
Instead of hiring a full in-house IT department, GoCo’s team works as your strategic technology partner**,** delivering:
- Expert configuration and monitoring of SMB and network protocols
- Regular security audits and patch management
- Compliance alignment with SOC 2, HIPAA, and ISO 27001
- 24/7 endpoint protection and threat detection
- Automated response systems that reduce human error
You get enterprise-level protection without the enterprise-level payroll.
Your Next Step Toward Zero-Trust
You don’t have to rebuild your entire infrastructure overnight. Start small:
- Audit your SMB configurations.
- Segment your network.
- Enable MFA and encryption.
- Partner with experts who live and breathe this every day.
Because when it comes to cybersecurity, trust is no longer a default; it’s an achievement.
Ready to take the next step?
Let’s build a Zero-Trust roadmap for your business, one that secures your operations, strengthens compliance, and empowers your growth.
Talk to a GoCo security expert today.
—-
If you found this article helpful, be sure to visit our latest piece on our Blog for more insights.
Technology decisions shouldn't be based on trends, they should support better business outcomes.
Explore our latest LinkedIn articles, where we share practical insights on Managed IT Services, cybersecurity, governance, operational excellence, and the strategies helping businesses reduce risk and scale with confidence.
Because better decisions start with better understanding.
Good Company IT
GoCo
You are in Good Company