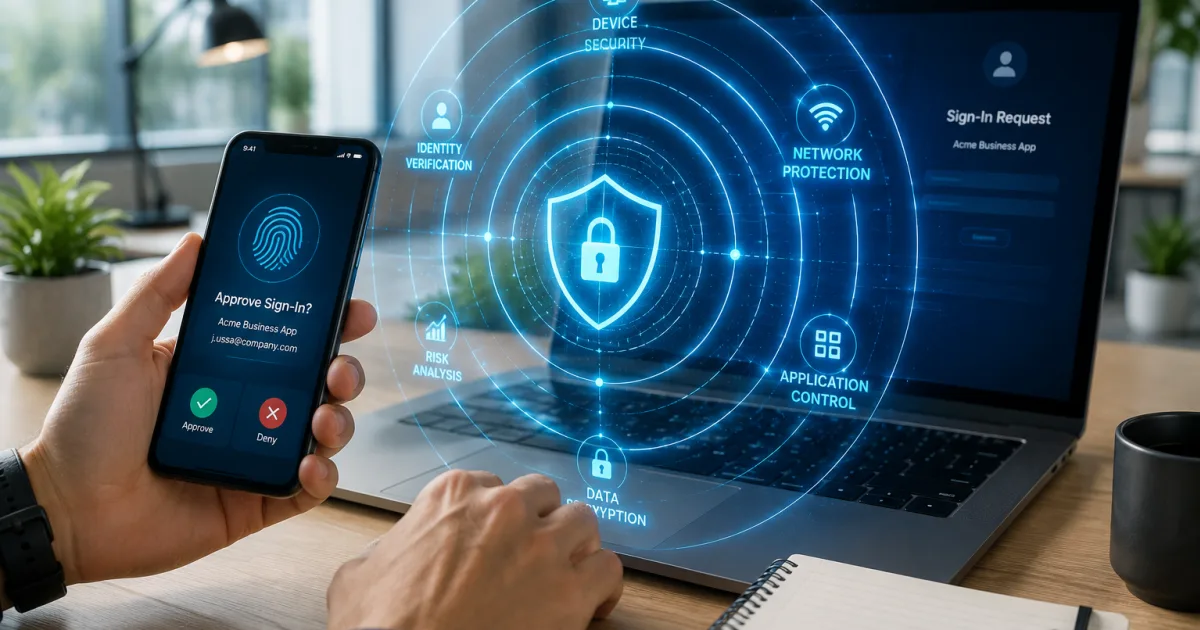
Multi-Factor Authentication MFA: Ultimate Security Guide | GoCo
Multi-Factor Authentication MFA is essential, but not enough. Learn layered security strategies to protect your IT systems. Discover more 🔐
SEO Title: Multi-Factor Authentication MFA: Ultimate Security Guide | GoCo
Meta Description: Multi-Factor Authentication MFA is essential, but not enough. Learn layered security strategies to protect your IT systems. Discover more 🔐
Most companies believe they are secure once Multi-Factor Authentication (MFA) is enabled. And for a moment, it feels like enough.
An extra verification step.
A second layer of identity confirmation.
A visible improvement over passwords alone.
But here’s the problem: Attackers are not targeting just passwords anymore. They are targeting the entire system around them.
That’s where the misconception begins.
What Multi-Factor Authentication MFA Actually Solves
Multi-Factor Authentication MFA is designed to reduce the risk of unauthorized access by requiring more than one verification factor:
- Something you know (password)
- Something you have (device, token)
- Something you are (biometrics)
This significantly improves security compared to single-factor authentication.
However, MFA only protects one layer:
H3. Identity verification at login.
It does not protect:
- What happens after access is granted
- How permissions are structured
- How systems are monitored
- How devices are secured
And that’s where most risks exist.
The False Sense of Security
Many organizations implement MFA and assume their environment is protected. But attackers adapt.
Common attack methods today include:
- MFA fatigue attacks (repeated push notifications until approved)
- Session hijacking after login
- Compromised endpoints with valid credentials
- Misconfigured access permissions
In these cases, MFA is not bypassed. It is simply not enough.
What Is Layered Security?
Layered security, also known as defense in depth, is the practice of applying multiple security controls across different parts of an IT environment.
Instead of relying on a single control, it creates overlapping protection across:
- Identity
- Devices
- Network
- Applications
- Data
If one layer fails, another one compensates. This is what makes systems resilient.
The Key Layers Beyond MFA
1. Identity and Access Management (IAM)
MFA is part of identity security — but not the whole solution. You also need:
- Role-based access control (RBAC)
- Regular access reviews
- Least-privilege principles
Users should only have access to what they need, nothing more.
2. Endpoint Security
If a device is compromised, MFA becomes irrelevant. Endpoint security includes:
- Endpoint Detection and Response (EDR)
- Device encryption
- Patch management
Every device must be treated as a potential entry point.
3. Continuous Monitoring
Security is not a one-time setup. You need visibility into:
- Login behavior
- System activity
- Anomalies and alerts
Without monitoring, threats go unnoticed.
4. Secure Configuration of Tools
Many breaches don’t happen because of weak tools. They happen because of misconfigured ones.
Cloud platforms, collaboration tools, and internal systems must be:
- Properly configured
- Regularly audited
- Aligned with security policies
Technology is only as secure as its configuration.
5. Incident Response Readiness
Even with strong controls, incidents can happen. What matters is how quickly and effectively you respond.
A structured response includes:
- Defined roles and responsibilities
- Clear escalation paths
- Documented procedures
Without a plan, response becomes reactive and slow.
Why Layered Security Matters for Growing Companies
As organizations grow, their attack surface expands:
- More users
- More devices
- More integrations
Each new element introduces potential risk. Relying on a single control like MFA in this context is not scalable.
Layered security ensures that growth does not compromise protection.
Final Insight
Multi-Factor Authentication MFA is essential. But it is only one piece of a larger system.
Security is not defined by a single control. It is defined by how multiple controls work together.
If your organization relies on MFA as its primary defense, you are protecting the front door — but leaving the rest of the building exposed.
Real security comes from structure, visibility, and layered execution. Because in modern IT environments, protection is not about adding more tools.
It’s about building a system that works, even when one layer fails.
You’re in Good Company.